Vulnerability Remediation
Your code keeps growing. Your security debt doesn't have to.
Agent takes every important CVE from your scanners and opens a tested fix PR in every affected repo, routed to the owning team. With no upstream fix it files the mitigation and comes back when one is available.
WORKS WITH

Weeks → hrs
Time-to-patch
1 → N
One fix, every affected repo
0%
Hallucination rate
66%
Runs cheaper from reused memories
HOW It RUNS
Your scanner found it, nobody fixed it
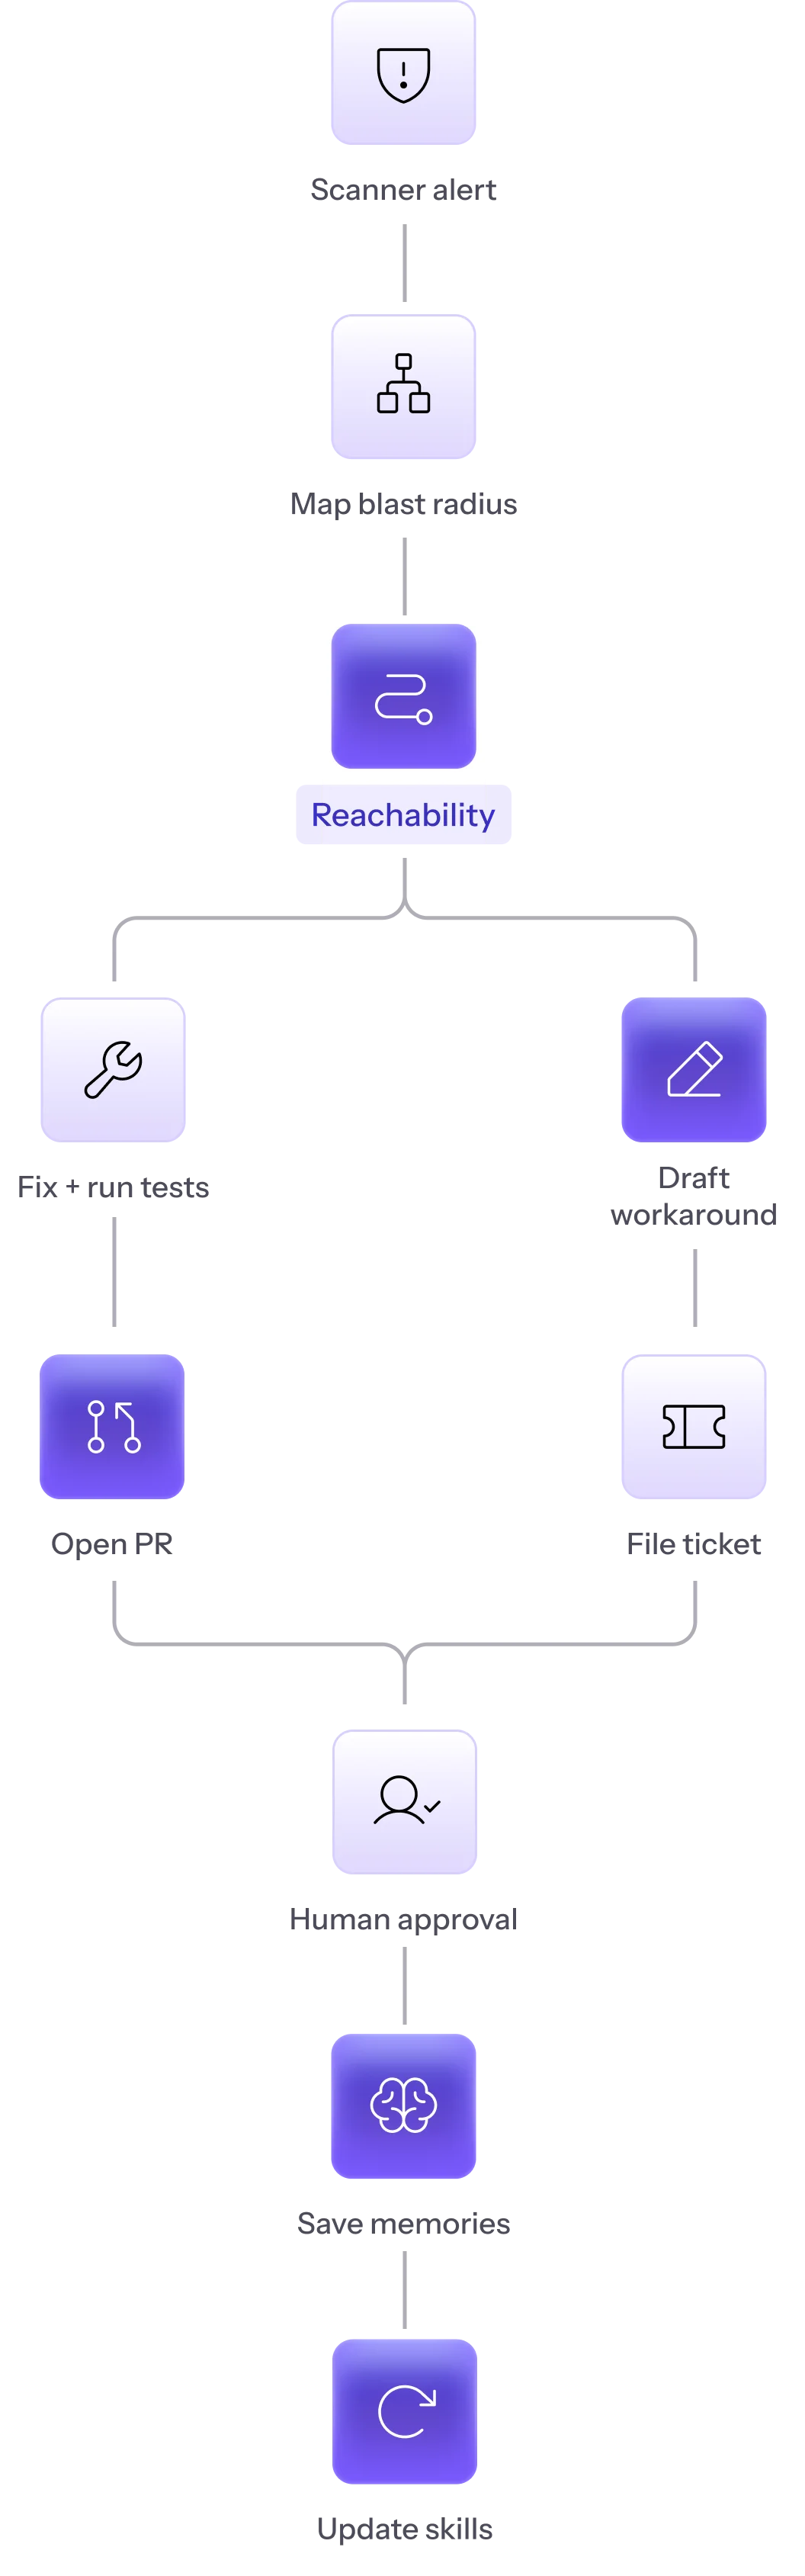
Understands your service code across repos, traces each CVE to the services that can actually reach it, opens a tested fix PR for the owning team, and gets better with every run.

Built for Platform Engineering & AppSec
Four jobs the agent takes off the security backlog
A tested bump that passes CI
The agent finds the smallest upgrade (patch, then minor, then major) that fixes the CVE, updates the lockfile, tests for breakage, and opens a draft PR with failures and changelog notes.
One CVE, twelve repos, twelve PRs
The same library shows up across services, base images and Terraform modules. The agent opens a PR for each repo, learning from the first fix so the eleventh costs less.
The evidence chain auditors ask for
For regulated teams, every CVE has a severity-based SLA and an evidence trail from detection to clean rescan—ready for PCI DSS, DORA, and FFIEC audits without last-minute reconstruction.
Self-improvement loop runs autonomously
Library upgrades teach costly lessons: what broke the build, which version fixed it, what the changelog actually meant. The agent saves those lessons in shared context, and your evals score each run.


