Incident Response
Cut MTTR from 2 hours to 15 minutes
Triages every alert and has root cause ready before on-call picks up the page. Below P1 it opens the fix PR and routes it to the owning team.
WORKS WITH

60-80%
MTTR reduction
Days→mins
Days→ mins
Postmortem
50%
Root cause with no developer wait
0
SLA breaches
HOW It RUNS
Deterministic where it should be, agentic where it pays
Alert grouping stays rule-based and cheap to run. Triage, investigation and remediation go to agents that improve every run, and a P1 gate decides whether anyone is paged.
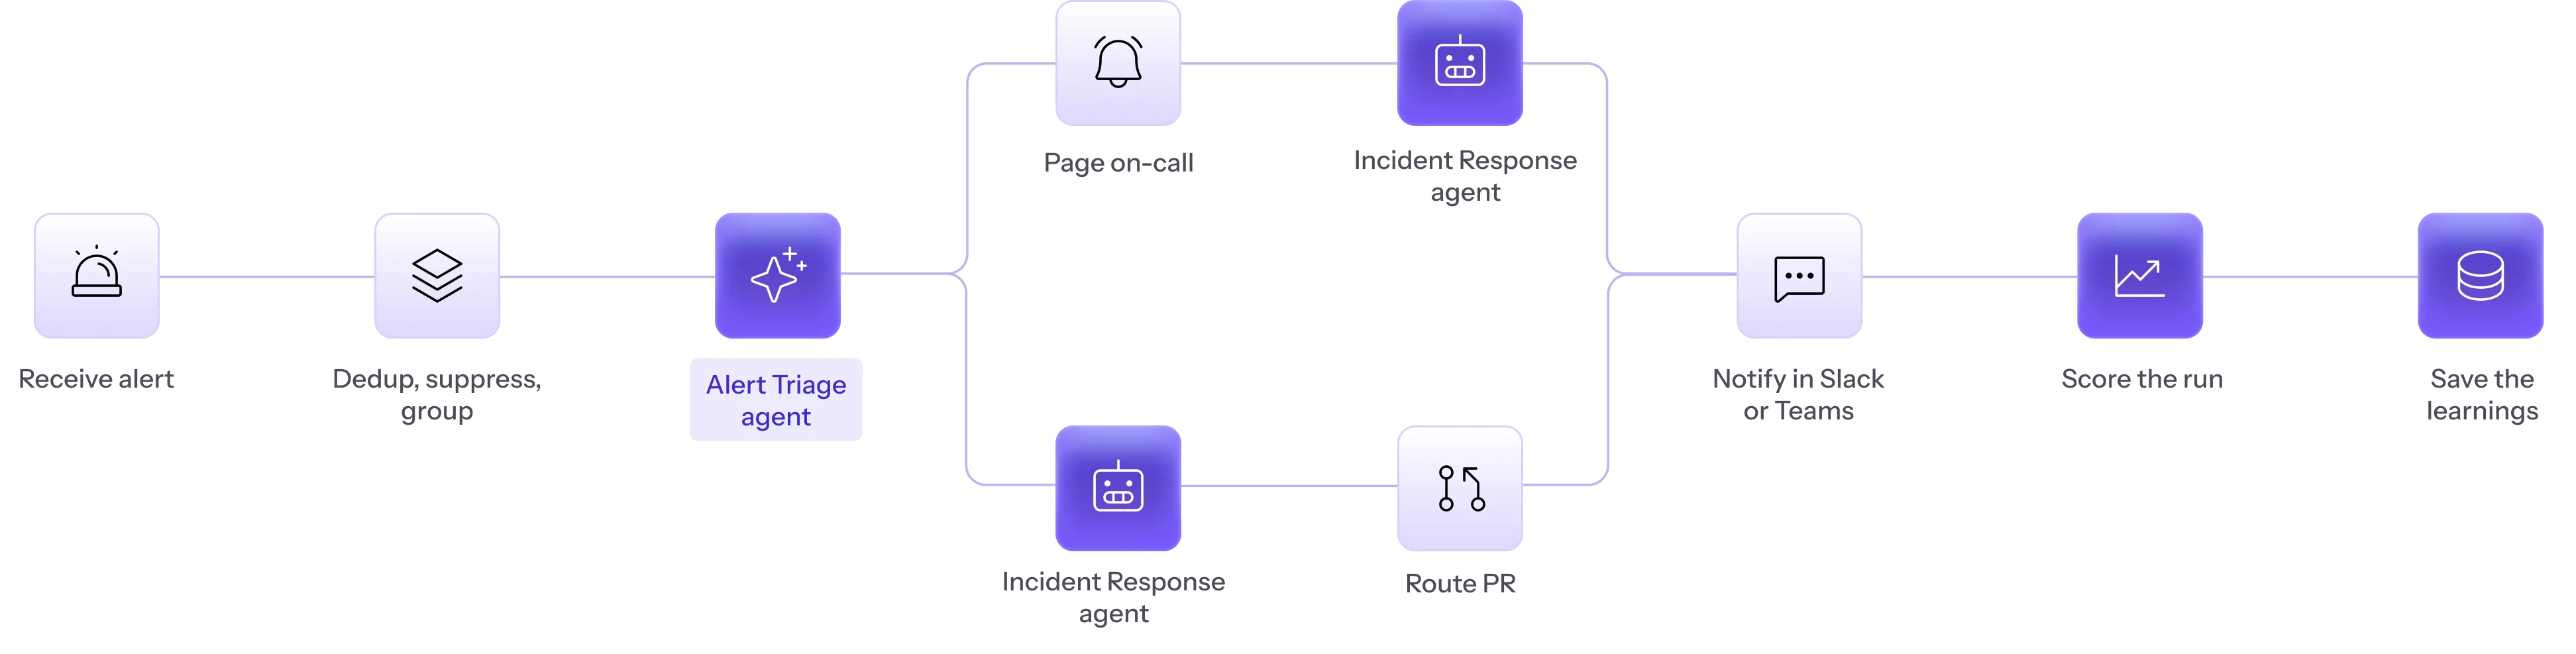
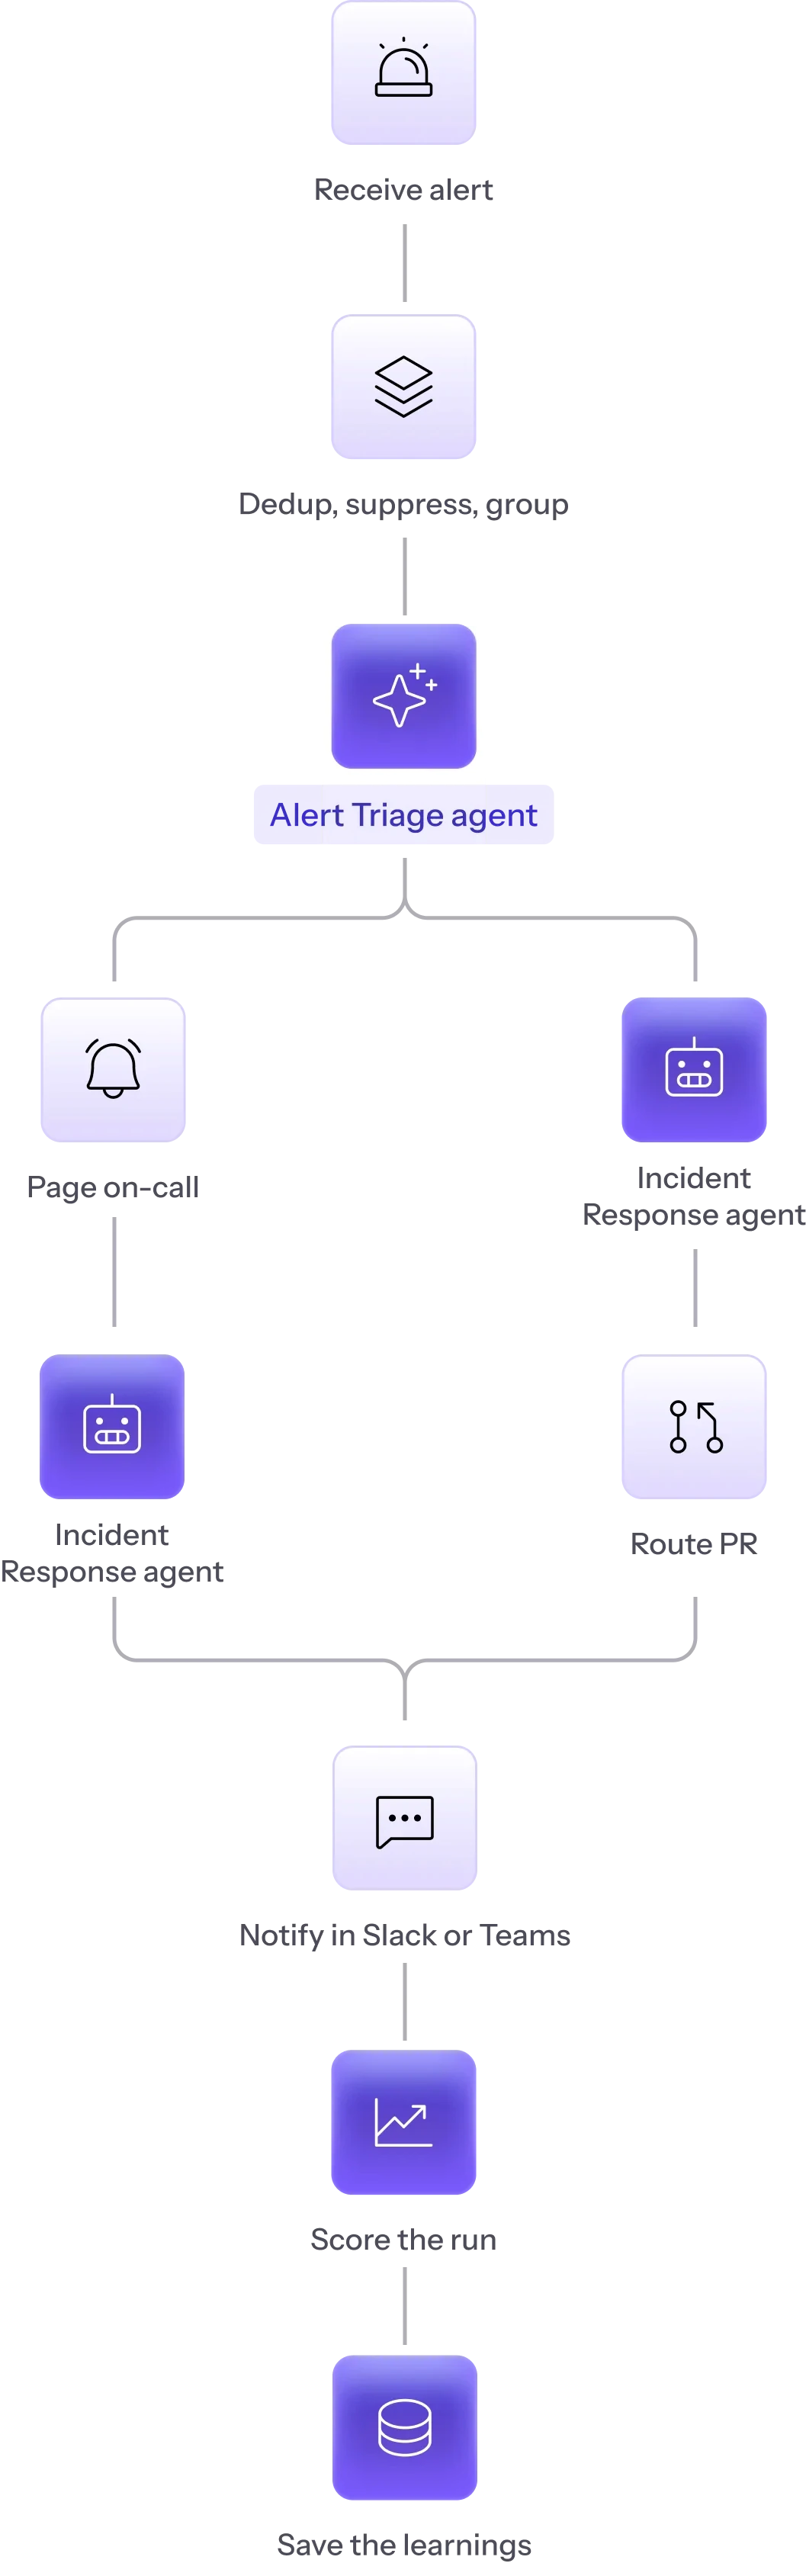
Every incident, investigated before anyone is paged
Every incident, investigated before anyone is paged
Routing
Context
Knowledge
Outcome
Without Autoheal
Every alert pages a human, so SREs triage noise at 3 a.m.
Evidence spread across six systems, and a developer pulled in to correlate it.
SOPs go stale, and tuning the triage rules is somebody's side project.
MTTR in hours, postmortem in days written from memory.
With Autoheal
Dedup, grouping and triage run first, so only P1s wake someone.
Logs, traces, deploys and diffs correlated into one root-cause report, with no developer wait.
Memories captured from every run and spec changes scored before they ship.
MTTR in minutes, postmortem in the same session, with the fix PR attached.
Routing
Every alert pages a human, so SREs triage noise at 3 a.m.
Dedup, grouping and triage run first, so only P1s wake someone.
Context
Evidence spread across six systems, and a developer pulled in to correlate it.
Logs, traces, deploys and diffs correlated into one root-cause report, with no developer wait.
Knowledge
SOPs go stale, and tuning the triage rules is somebody's side project.
Memories captured from every run and spec changes scored before they ship.
Outcome
MTTR in hours, postmortem in days written from memory.
MTTR in minutes, postmortem in the same session, with the fix PR attached.
Built for SRE & Platform Engineering
Four jobs the agent takes off the on-call rotation
Root cause before on-call opens a laptop
By the time the page fires, the investigation is underway—linking the preceding deploy, its diff, and changed log clusters, with evidence posted to the channel.
Fixes arrive as pull requests for review
Below P1 the agent branches, applies the fix, runs the tests in a sandbox and opens a PR against the owning repo. Merge stays with the team, and it has no write access to main.
Postmortems drafted from the real timeline
Every resolved incident drafts a postmortem from actual events—timeline, contributing factors, and action items prefilled. No reconstruction from memory.
Self-improvement loop runs autonomously
An SRE downgrading a P1 teaches the agent a lesson most tools lose. Here, the override updates shared context, and the run is scored against your evals.
PLATFORM
Runs where you run, on the harness and models you approve
Runs on the same platform as the Release Readiness, Vulnerability Remediation and AI Coding Cost agents, inside your boundary and on models you have approved.
Bring your own harness
Use the built-in harness or the coding agents your teams already run, isolated in sandboxes you control.
Bring your own models
Route each task to the right model from your approved list, with the frontier model kept for the work that needs it.
Invoke it from where the team works
From your alerting webhook, the CLI, over MCP, or from the incident channel in Slack and Teams.
Enterprise-grade security and control, built for complex, regulated industries
Granular permissions, full audit trails, and compliance that meets all security needs, engineered for teams with zero margin for error.
Sovereign deployments
Deploy as SaaS or fully air-gapped in your own cloud. Control where harnesses and sandboxes run, using pre-approved models.
Governance policies
Every agent runs in isolated environments, with access to tools by policy. Set per-agent budgets and approval gates for every action.
Audit trails
Every action, decision, and change is logged, versioned, and reviewable - so teams can trace exactly what happened, when, and why.
Least-privileged integrations
Agents connect to your systems with only the access required for the task. Credentials are scoped, short-lived, and retrieved from your secrets manager.

ISO 27001
SOC 2
TYPE 2
SOC 2 Type II
Zero Data Retention
Enterprise-grade security and control, built for complex, regulated industries
Granular permissions, full audit trails, and compliance that meets all security needs, engineered for teams with zero margin for error.
Sovereign deployments
Deploy as SaaS or fully air-gapped in your own cloud. Control where harnesses and sandboxes run, using pre-approved models.
Governance policies
Every agent runs in isolated environments, with access to tools by policy. Set per-agent budgets and approval gates for every action.
Audit trails
Every action, decision, and change is logged, versioned, and reviewable - so teams can trace exactly what happened, when, and why.
Least-privileged integrations
Agents connect to your systems with only the access required for the task. Credentials are scoped, short-lived, and retrieved from your secrets manager.
ISO 27001
SOC 2
TYPE 2
SOC 2 Type II
Zero Data Retention
Enterprise-grade security and control, built for complex, regulated industries
Granular permissions, full audit trails, and compliance that meets all security needs, engineered for teams with zero margin for error.
Sovereign deployments
Deploy as SaaS or fully air-gapped in your own cloud. Control where harnesses and sandboxes run, using pre-approved models.
Governance policies
Every agent runs in isolated environments, with access to tools by policy. Set per-agent budgets and approval gates for every action.
Audit trails
Every action, decision, and change is logged, versioned, and reviewable - so teams can trace exactly what happened, when, and why.
Least-privileged integrations
Agents connect to your systems with only the access required for the task. Credentials are scoped, short-lived, and retrieved from your secrets manager.
ISO 27001
SOC 2
TYPE 2
SOC 2 Type II
Zero Data Retention
Enterprise-grade security and control, built for complex, regulated industries
Granular permissions, full audit trails, and compliance that meets all security needs, engineered for teams with zero margin for error.
Sovereign deployments
Deploy as SaaS or fully air-gapped in your own cloud. Control where harnesses and sandboxes run, using pre-approved models.
Governance policies
Every agent runs in isolated environments, with access to tools by policy. Set per-agent budgets and approval gates for every action.
Audit trails
Every action, decision, and change is logged, versioned, and reviewable - so teams can trace exactly what happened, when, and why.
Least-privileged integrations
Agents connect to your systems with only the access required for the task. Credentials are scoped, short-lived, and retrieved from your secrets manager.
ISO 27001
SOC 2
TYPE 2
SOC 2 Type II
Zero Data Retention
PLATFORM
Runs where you run, on the harness and models you approve
Runs on the same platform as the Incident Response, Release Readiness and Vulnerability Remediation agents, inside your boundary and on models you have approved.
Bring your own harness
Use the built-in harness or the coding agents your teams already run, isolated in sandboxes you control.
Bring your own models
Route each task to the right model from your approved list, with the frontier model kept for the work that needs it.
Invoke it from where the team works
From your alerting webhook, the CLI, over MCP, or from the incident channel in Slack and Teams.

Bring your agents in line, and go from chaos to clockwork
Every run makes the next one better. See it on your stack.
Bring your agents in line, and go from chaos to clockwork
Every run makes the next one better. See it on your stack.

Bring your agents in line, and go from chaos to clockwork
Every run makes the next one better. See it on your stack.
Bring your agents in line, and go from chaos to clockwork
Every run makes the next one better. See it on your stack.